Ben Weiss and Ryan Weeks
Binance said that the hackers behind a $US6.3 billion ($9 billion) heist used social engineering techniques including fake job interviews, as well as malicious software, in the most detailed report yet on how the incident unfolded.
Binance, which attributed the hack to North Korea, said the breach involved a “sophisticated, multi-stage campaign.” One of the company’s engineers was contacted through a job hunting platform by someone posing as a project director, the exchange said in the report. The employee was then interviewed by a person claiming to be the chief executive officer of a fictitious company over a social chat app, and asked to download an assignment containing a “malicious code repository.” This then set off a series of unauthorised activities, the report said.
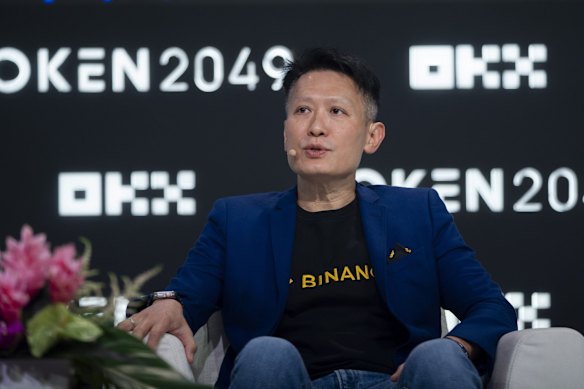
“This was not a single mistake or a single breach. It was a campaign built over many months,” said Richard Teng, co-chief executive officer of Binance. The attackers “combined fake recruitment interviews, malicious software disguised as legitimate developer tools, compromised devices, and AI techniques.”
Nine days before the hack, attackers tapped the laptop belonging to the employee lured into the fake job interview to infiltrate the computers of two more software engineers who worked on Binance’s digital wallets. The hackers used an “internal AI tool” to gain access, Binance’s report said, without specifying what the tool was or how it was used to gain control of the employees’ laptops.
One of those two engineers had in June accidentally downloaded malicious software in order to install what Binance called “a popular AI coding tool.” In doing so, they had exposed the nature of their role, as well as that of some colleagues who worked on Binance’s wallets to the hacker, according to the report.
The new disclosure on how hackers managed to siphon billions from Binance comes as the exchange — and the crypto industry — attempts to recover from the largest hack in the history of cyber thefts.
The breach deepened a mounting security crisis for a sector already grappling with a wave of cyberattacks. Artificial intelligence is adding to the threat, giving criminals new tools to find weaknesses and deceive employees, and raising the stakes for platforms safeguarding billions of dollars in digital assets.
Still, the techniques that hackers used to infiltrate Binance are tried-and-true strategies common to North Korea, according to law enforcement agencies and security researchers. In fact, the cybersecurity firm Palo Alto Networks coined the name “Contagious Interview” for the job-interview tactics.
In 2022, North Korean hackers used a fake job offer to trick an engineer for the crypto-powered game Axie Infinity and pull off a $US590 million heist. Three years later, the Democratic People’s Republic of Korea broke into the crypto exchange Bybit and stole $US1.5 billion, which was previously the largest digital assets heist in history, according to crypto analytics firms.
In the hours after the hack, first reported on October 29, Binance initially said that the attackers may have compromised a software engineer’s laptop, which allowed thieves to withdraw crypto from the exchange. In a subsequent post, the exchange said that the attack was “complex” and the company had “uncovered additional points of breach,” without providing more details.
Shortly after the exploit, traders, cybersecurity professionals, and token issuers all rushed to respond to the fallout. Stablecoin giants Tether and Circle Internet Group, as well as other entities, quickly froze — or stopped hackers from moving — almost $US3 billion in funds. Analytics firms raced to track the flow of crypto, eventually attributing the exploit to North Korea, a charge the country has denied. Some traders capitalised on the market turbulence.
Throughout the ordeal, Binance has sought to reassure its users, saying that it will bear the financial cost. Still, the exchange paused withdrawals for almost two days after the incident. Early on Sunday, Binance began to progressively let users take out funds. The company initially saw billions in outflows, but the situation appears to have stabilised and by Tuesday it reported that hourly deposits had started exceeding hourly withdrawals.
Binance has also said that it has almost replenished the cryptocurrency that the hackers had stolen, using a combination of money from its corporate treasury as well as two insurance funds.
The crypto exchange is also working with US law enforcement, including the Federal Bureau of Investigation, the US Secret Service, and the Justice Department. The FBI, which stepped in soon after the hack in Binance’s aid, has also attributed the breach to North Korean hackers.
In 2026, Binance identified and prevented 57 attempted attacks from hackers connected to North Korea, the exchange said in its report detailing the cyber theft. The company has also said that it has implemented various mitigation measures after the hack, including rebuilding the affected crypto infrastructure, redeveloping the internal AI tool, as well as enhancing security scans and an AI-powered detector.
Despite the history-making hack, the market fallout has remained muted. Initially, Bitcoin fell more than 4 per cent after the exploit to nearly $US76,000, but the world’s largest cryptocurrency has since pared back some of its losses, trading at around $US77,600.
From our partners
Disclaimer : This story is auto aggregated by a computer programme and has not been created or edited by DOWNTHENEWS. Publisher: www.smh.com.au